PDCA
What is PDCA?
PDCA is a method for continuous process improvement. The abbreviation stands for Plan, Do, Check and Act. By constantly repeating these four steps, organizations can implement and secure structured improvements. The method is widely used within quality management and is an important principle within ISO 9001, among others.
When do you use the PDCA cycle?
The PDCA cycle is used when you want to improve or better control processes.
Typical applications are:
- Improving work processes
- Performing quality checks
- Implementing process improvements
- Fixing recurring errors
The cycle is repeatable, creating continuous improvement.
The 4 steps briefly explained
The PDCA cycle consists of four steps. In the Plan phase, you analyze the current situation and draw up an improvement plan. In the Do phase, you implement this improvement, often first on a small scale. Then, in the Check phase, you check whether the change produces the desired result. In the Act phase you secure the improvement or make adjustments, after which the cycle begins again.
PDCA cycle in practice
One organization finds that inspections are not always completed in full.
- Plan: Investigate where this is going wrong and determine how to clarify the process.
- Do: Implement a modified inspection procedure.
- Check: Check that inspections are performed more completely and fewer steps are skipped.
- Act: Establish the new practice as a standard or further adjust as needed.
Continuous improvement in practice
Digital tools can help apply the PDCA cycle effectively. Recording processes and registrations digitally provides better insight into results and areas for improvement. LeanForms supports organizations with digital forms and workflows that make it easier to improve and secure processes.
FAQ
These are the questions we hear most often about PDCA, with answers.
Yes, the PDCA cycle is often called the Deming cycle, after William Edwards Deming who popularized the method.
Not literally, but the principle of continuous improvement is an important basis of the standard.
Yes, the method is suitable for both small and large improvements.
PDCA is a general method for continuous improvement and is widely used within quality management. DMAIC is a more structured approach from Six Sigma, with the steps Define, Measure, Analyze, Improve and Control. Both methods focus on process improvement, but DMAIC is often used in more complex data analysis and optimization projects.
Related items

Certifications and audits: more than just a checkmark on a checklist
Audits and certifications have played an important role in the business world for decades. ISO 9001 was first published in 1987. Since then, the standards landscape has expanded: organizations are now assessed not only on quality, but also on topics such as the environment, working conditions, sustainability, ethics, and corporate social responsibility.
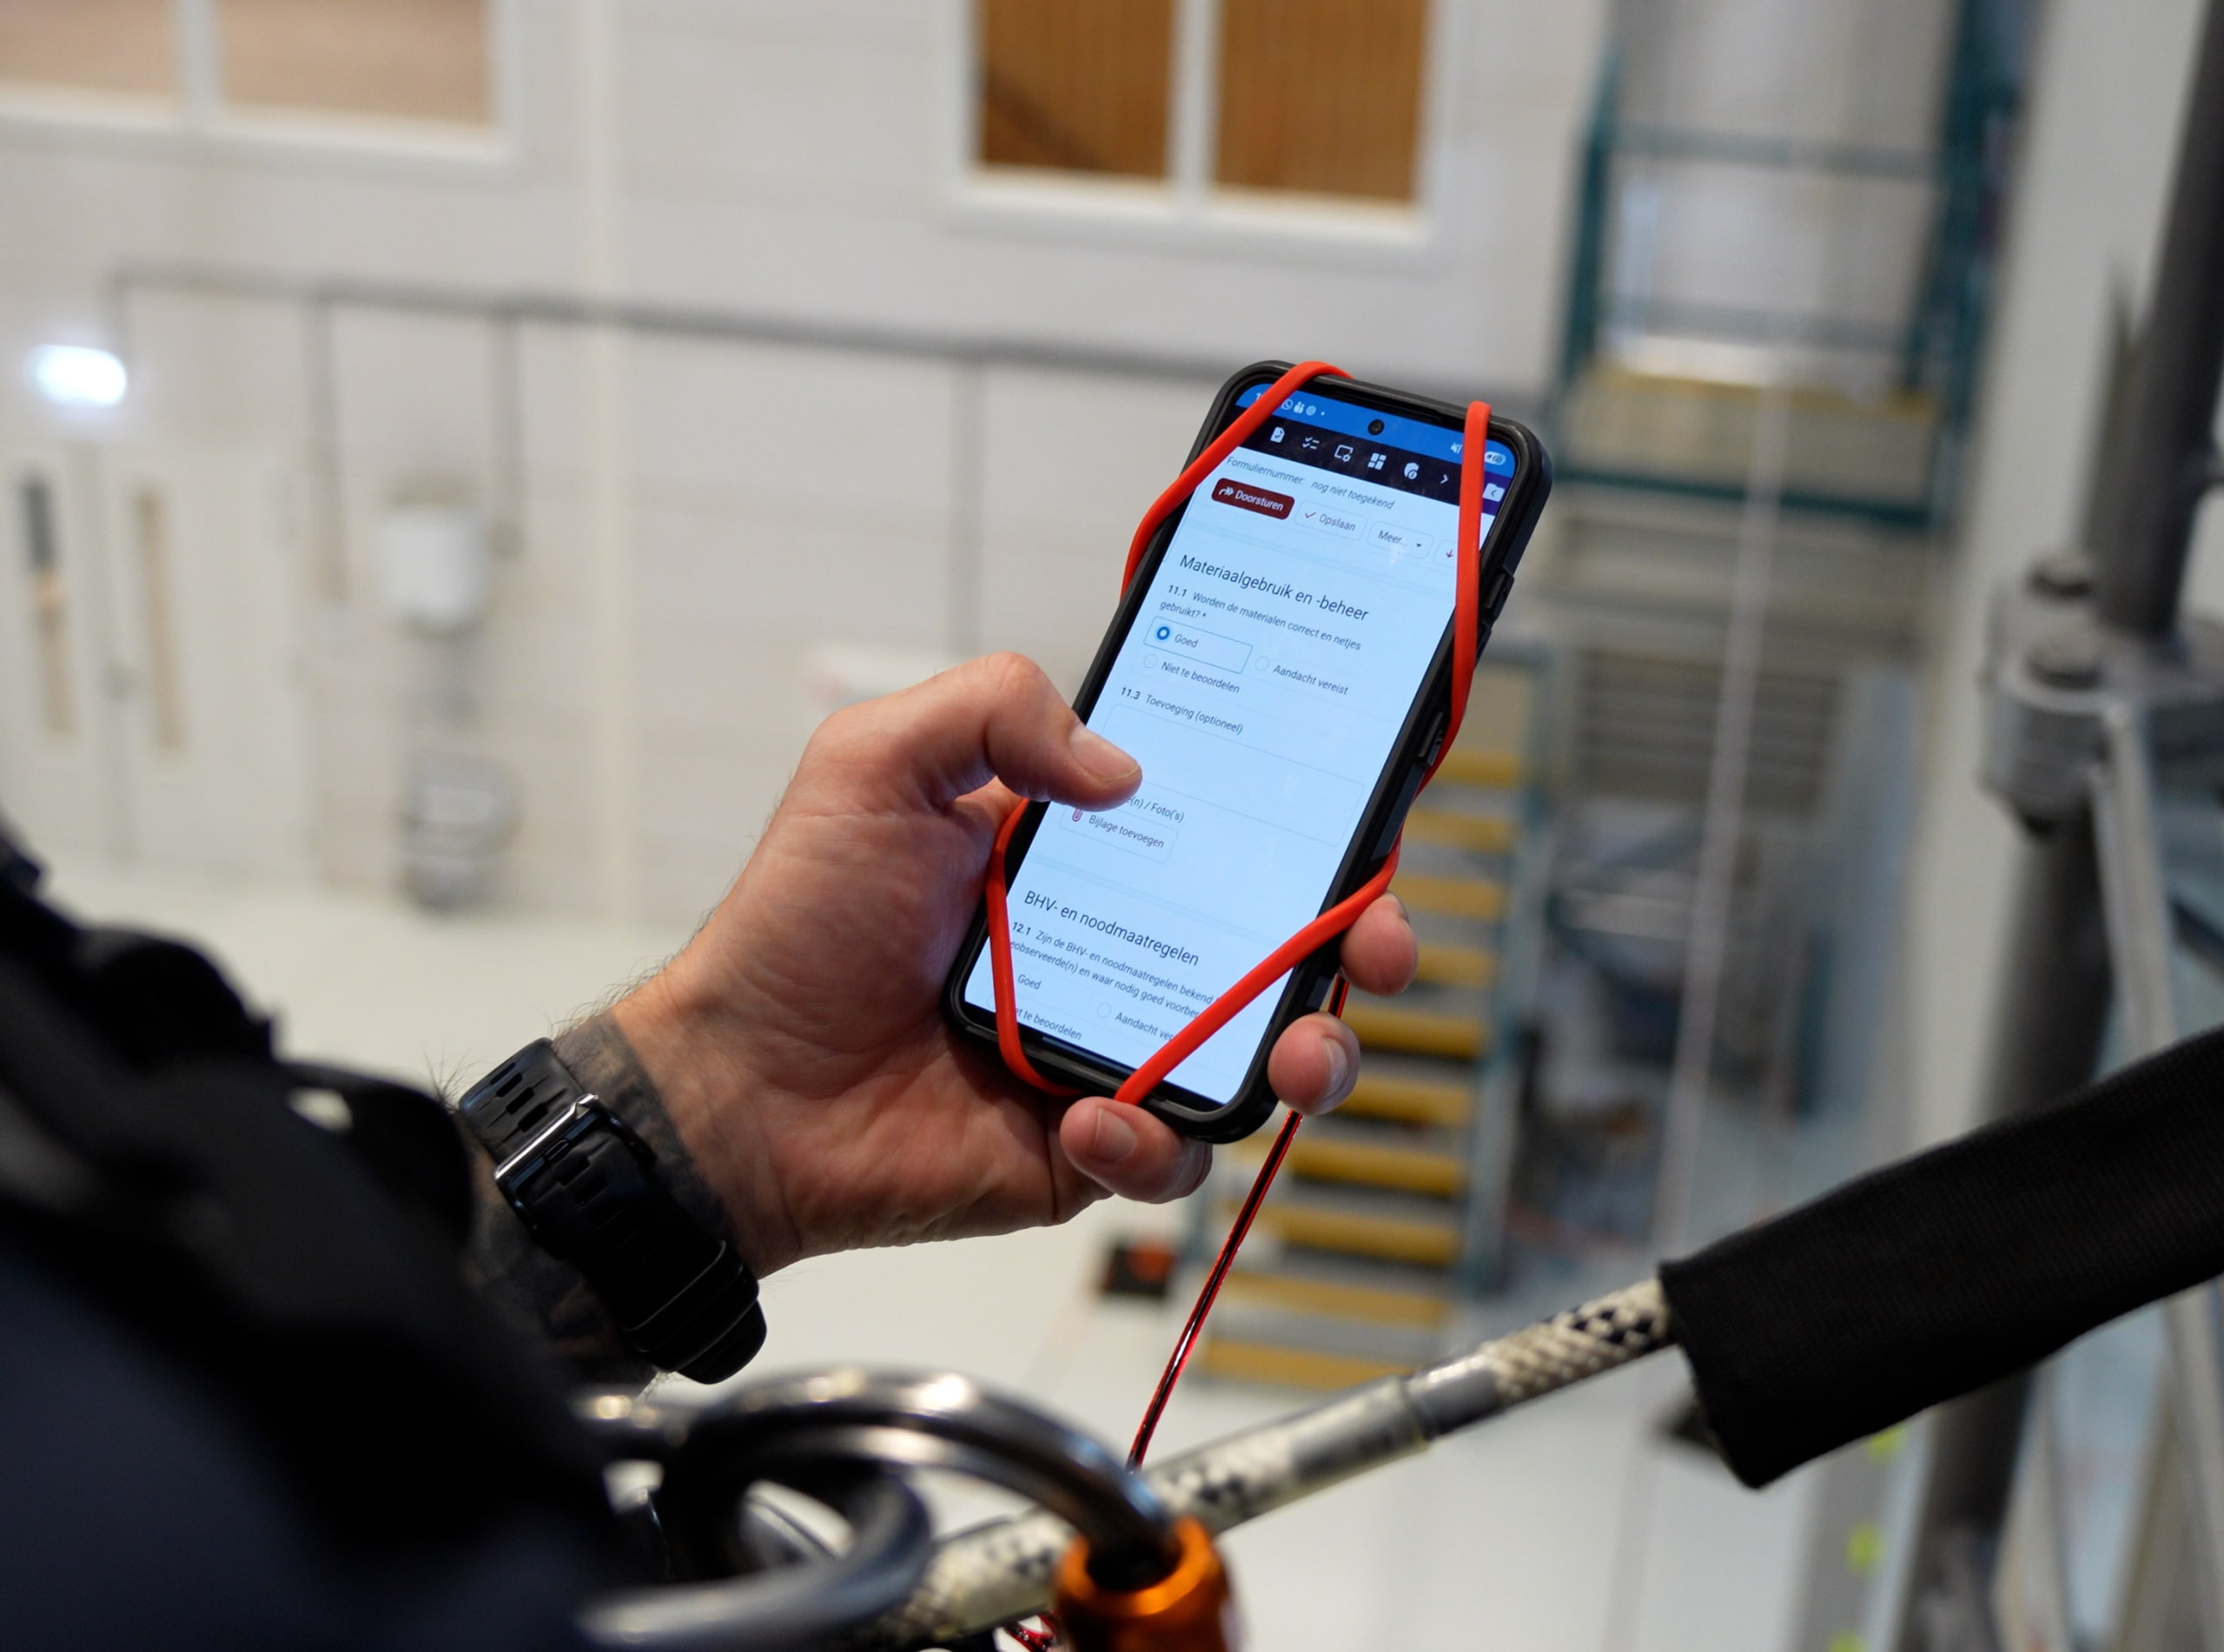
Customer Testimonial: Eurosafe
How does Eurosafe use LeanForms for risk assessments of confined spaces? Learn how experts document their findings and work toward standardized reporting.
ISO 9001:2026: Change or Real Improvement?
ISO 9001:2026 will be published on September 16, 2026. What changes are being made, and what do they mean for your quality management system?
NIS2 and Dutch SMEs
Cybersecurity has long since ceased to be a matter solely for the IT department. With the enactment of the Cybersecurity Act, digital resilience has explicitly become the responsibility of board members and executive management.
Want to know more? Get in touch
Do you have questions or are you curious how LeanForms can support your organization? We are ready to answer all your questions! Get instant specialized advice on the best solution for your specific situation.